Illustrative materialsThe bound file an audit is written into
EU AI ActNIST AI RMFGDPRNYC Local Law 144California FEHA (Automated Decision Systems)Colorado AI Law (SB 26-189)Colorado SB 21-169NAIC AI PrinciplesTexas AI ActSingapore PDPAHIPAANIST CSFCCPA / CPRADORAOECD AI PrinciplesCIS ControlsAI EthicsFTC AI GuidanceBahrain PDPLQatar PDPLSaudi PDPLUAE PDPLQuebec Law 25SR 26-2 / OCC 2026-13SS1/23 (PRA)OSFI E-23
EU AI ActNIST AI RMFGDPRNYC Local Law 144California FEHA (Automated Decision Systems)Colorado AI Law (SB 26-189)Colorado SB 21-169NAIC AI PrinciplesTexas AI ActSingapore PDPAHIPAANIST CSFCCPA / CPRADORAOECD AI PrinciplesCIS ControlsAI EthicsFTC AI GuidanceBahrain PDPLQatar PDPLSaudi PDPLUAE PDPLQuebec Law 25SR 26-2 / OCC 2026-13SS1/23 (PRA)OSFI E-23
The regulatory landscape
The rules are already live
All 31 frameworks an iDharma audit can assess you against - binding regulation, voluntary standards, and supervisory guidance. Every finding is mapped to the specific obligation it touches, so you know which rule a gap sits under, not just that a gap exists.
Phasing in
EU AI Act
European Union
Conformity assessments, technical documentation, and ongoing monitoring for high-risk systems.
Status and scope verified against each framework's primary source. We cite enforcement figures only once confirmed from the original filing - verified cases appear in our teardowns.
What is an AI Audit?
A structured review of every AI system your organization relies on.
An AI audit isn't about finding fault, it's about clarity: we map what your AI tools actually do, identify the regulations that apply, and hand you a prioritized action plan you can act on immediately.
01
Know your exposure
Understand where your AI stands before enforcement, a partner bank, or a procurement team asks.
02
Win enterprise contracts
Procurement teams now demand AI compliance evidence. An audit gives you a credible answer.
03
Build customer trust
Show clients and partners how their data is protected and how decisions are made.
04
Scale confidently
Deploy new AI capabilities knowing your compliance baseline is documented and current.
Every audit is scoped to your systems and your sector - nothing is charged until you approve the scope.
Most consultancies offer a generic checklist. iDharma delivers a structured, sector-specific, actionable audit.
What You Get
iDharma Audit
Generic Consultancy
DIY Checklist
Sector-specific risk mapping
Built-in
Partial
EU AI Act risk classification
All tiers
Basic
Plain-language action plan
Prioritized
Legal language
Remediation guidance included
Extra cost
Delivered in 1–4 weeks
Scoped per engagement
Self-paced
Evidence pack for regulators
Included
Optional
Fixed transparent pricing
Time & materials
How We're Paid
What we find never changes what we're paid.
We don’t build or sell the AI we assess, and we don’t sell the fixes we’d recommend.
We’re paid to assess your system honestly against a published standard - not to reach a particular conclusion.
We disclose any relationship that could color the work, and if a genuine conflict exists, we decline the engagement rather than caveat it.
Audit Dimensions
Five areas we examine in every audit.
Each dimension maps to a specific regulatory obligation - and to a business risk you can actually manage.
Together they cover how your AI is governed, where its data comes from, whether it treats people fairly, how it holds up under pressure, and whether it meets the law.
An iDharma audit is scoped against the specific instruments that apply to you - 31 of them, from binding regulation to the standards procurement asks about. Filter the set, or open any one to see what it requires and what an audit covers against it.
These pages describe what each instrument requires and what an audit covers against it. They are scoping guidance, not legal advice - iDharma works alongside your counsel, not in place of them.
Everything on this ladder is a private assessment. You get the
findings; nothing is published and nothing is maintained afterwards.
A framework audit - NYC Local Law 144, the EU AI Act, ISO/IEC 42001 - produces a
document the law makes public, and we keep it valid for twelve months: the
published summary, the candidate notice where one is required, a 60-day expiry
warning and a quarterly check that the summary is still live and linked.
That upkeep is the difference, not the depth of the testing.
Already have an audit you are not sure about?
$3,500 flat - an independent review of an
audit somebody else has already published, one tool. Credited in full against a
full audit booked within 90 days.
No payment until you approve the scope.
All audits are covered by NDA as standard. Your systems and data never leave the engagement.
FAQ
Questions we hear every time.
1
Scope & your involvement
Do we need to share our source code?
No. We work from system documentation, data flow diagrams, policy documents, and structured interviews with your team. Source code is never required for a compliance audit.
We're a small team - how much of our time does this take?
Typically around 3 hours of your team's time spread across the first four days - mostly answering our structured questionnaire and joining one call. We do the analysis independently.
What if we don't know which AI tools we're using?
That's exactly what the scoping call is for. Many clients discover AI systems embedded in third-party SaaS tools they didn't realise were in scope. We help you map your full AI footprint first.
2
Regulations & frameworks
Does the EU AI Act apply to us if we're outside the EU?
Yes - but not on the trigger most teams assume. The Act reaches you if you place an AI system on the EU market or put it into service there, or if the output your system produces is used in the EU, regardless of where your organization is registered. Processing personal data of EU residents is GDPR's trigger, not the AI Act's - the two catch different things, and a system can be in scope for one and not the other.
What frameworks do you audit against?
We cover the EU AI Act (all risk tiers), NIST AI RMF, ISO/IEC 42001, HIPAA, SOC 2, and India's DPDP, plus GDPR Articles 13, 14, and 22 - mapped to your specific use case.
Is this the same as a GDPR Data Protection Impact Assessment?
No, but our audit often surfaces what's needed for a DPIA. An AI compliance audit is broader - it covers the AI Act, sector rules, and operational risk - not just data protection law.
3
After the report
What happens after we get the report?
You receive 14 business days of written follow-up in your portal with your audit lead, plus optional remediation support packages if you want help implementing fixes - policy drafting, technical controls, staff training.
Can we use the report with enterprise clients or procurement teams?
Yes - the evidence pack is specifically designed to be shared with procurement teams, due diligence processes, and enterprise clients who require AI compliance documentation as part of vendor qualification.
4
Why iDharma
How is iDharma different from a law firm?
Law firms deliver legal opinions. We deliver operational compliance - structured evidence, actionable fixes, and plain-language guidance your technical and business teams can act on. We're not a substitute for legal counsel, but we work alongside yours.
Is there a guarantee?
We deliver within the scope and timeline we agree with you (typically 1–4 weeks). And if a regulator questions the methodology of our audit, we'll provide expert support at no additional cost.
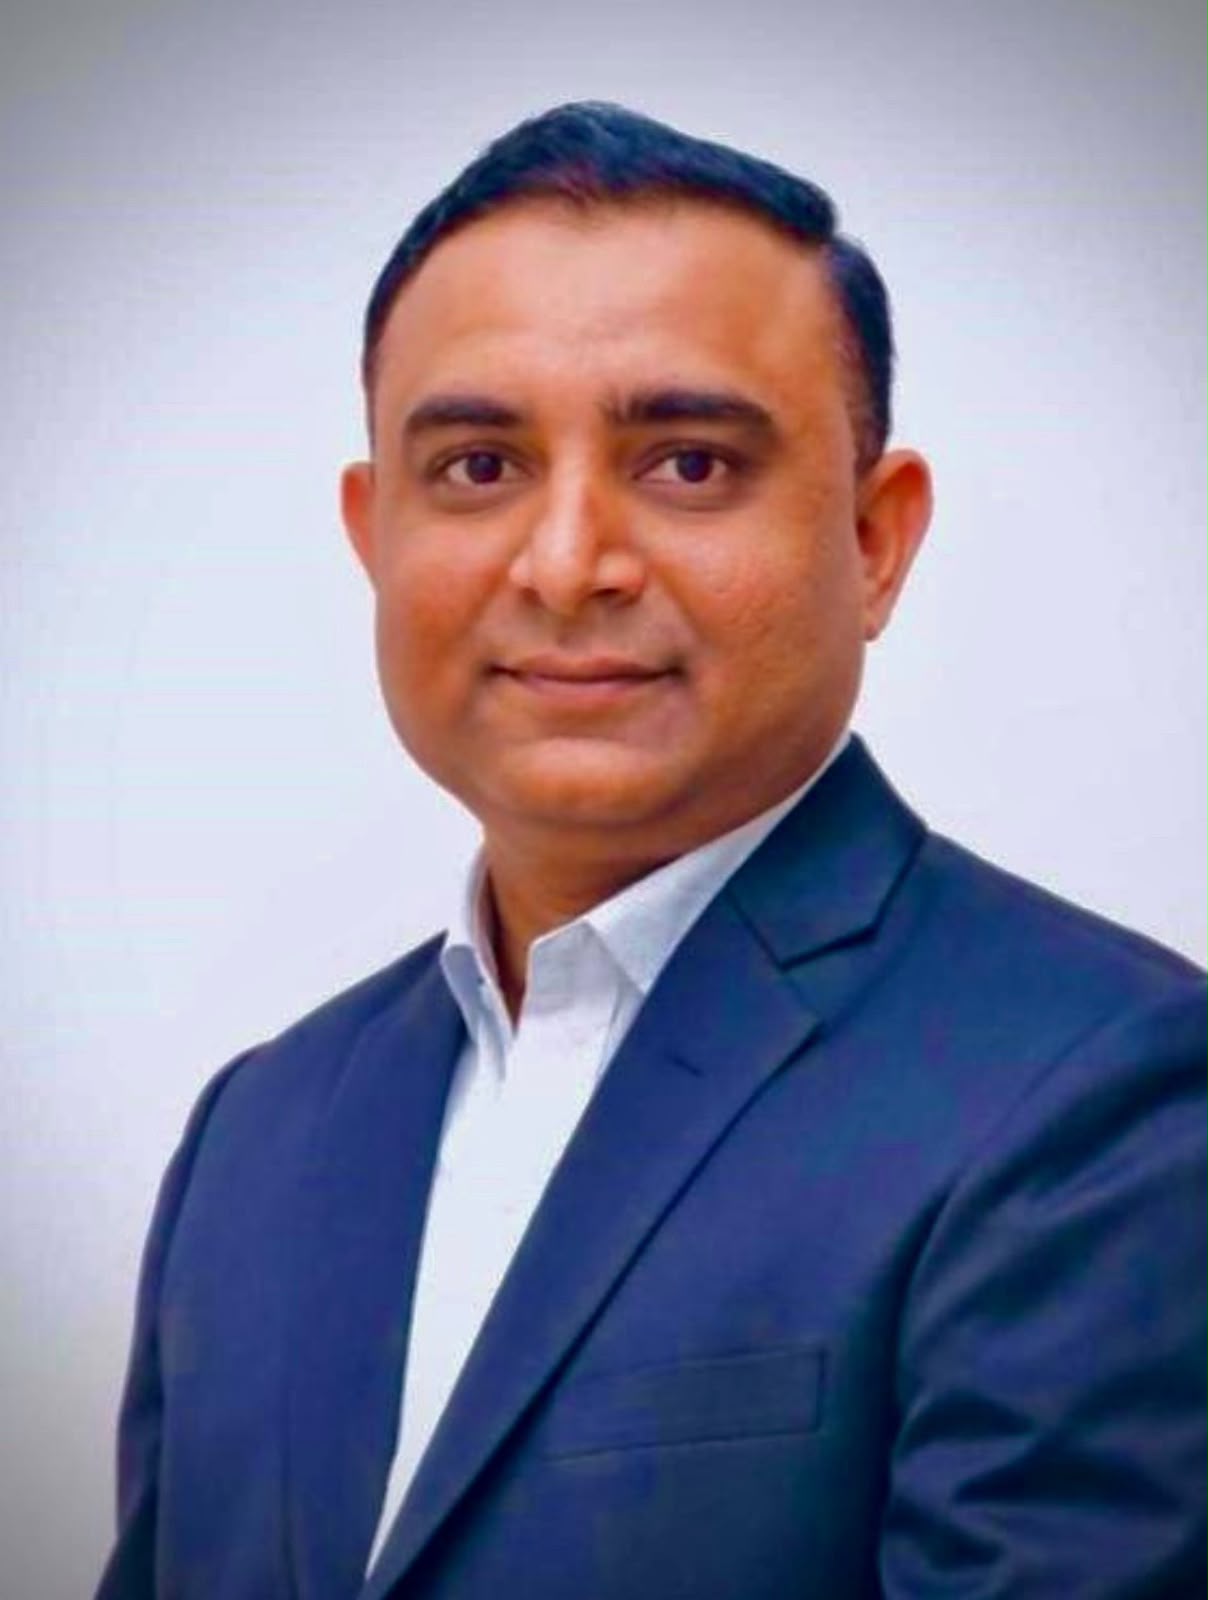
Your audit lead
✓ Named on every report
✓ Signs each audit personally
Who reviews your AI
Brijesh Patel
Founder & Lead Auditor
Every audit is led and signed by a named reviewer - no black box, no anonymous “team.”